
Intel Developer Forum Fall 2003 – Day 1: Otellini's Keynote
- Posted in
- IT Computing
Afterwards, they quickly moved on to their third “T”, LaGrande Technology. While Intel has previously mentioned LaGrande, this time we got a demo. While the acting abilities of the Intel staff need a little work, the technology looks very cool. The premise of the demo was keeping a hacker from being able to access information even after he has breached the users system. For instance, using LT combined with future Microsoft secure operating system technology, “secure” windows can pop up that aren't accessible via framebuffer grabbers.
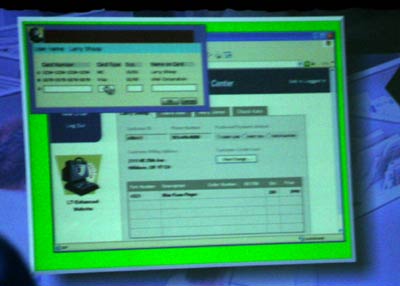
LaGrande in action
The same goes for the keyboard buffer, so it's not possible to sniff out what the user types. Even if the hacker does a full memory dump, Intel made it sound like memory was made to have less special associativity. In other words, when the name of someone is next to a credit card number on the screen, the credit card number is somewhere else in memory that cannot be reached (as easily).
When LaGrande was first announced, there was a bit of an uproar about privacy protection, which Otellini addressed in this keynote. Users will be able to enable/disable LaGrande technology at the hardware level if they would like, and we wouldn't have it any other way.
Originally published at https://www.anandtech.com/show/1149 (Wayback Machine).